As businesses increasingly depend on cloud platforms, connected devices, and digital networks, maintaining strong cybersecurity has become essential. A managed security service provider helps organizations monitor, protect, and manage their IT environments while addressing potential security risks more efficiently.
What Is a Managed Security Service Provider?
A managed security service provider (MSSP) is a specialized technology partner that delivers ongoing cybersecurity monitoring and protection. Instead of handling every security function internally, businesses can rely on an experienced provider for services such as threat monitoring, network security, vulnerability management, and security response.
This approach can be particularly valuable for businesses that need dependable protection but may not have the resources to maintain a dedicated cybersecurity team.
Why Businesses Need Managed Security Services
Cybersecurity threats can affect businesses of every size. Unauthorized access, malware, phishing attempts, network vulnerabilities, and other security risks can disrupt operations and potentially expose valuable business information.
A managed security service provider can help businesses establish continuous security monitoring and respond to potential threats in a structured manner. Proactive monitoring can also help identify unusual activity before it develops into a more significant security issue.
Key Services Offered by an MSSP
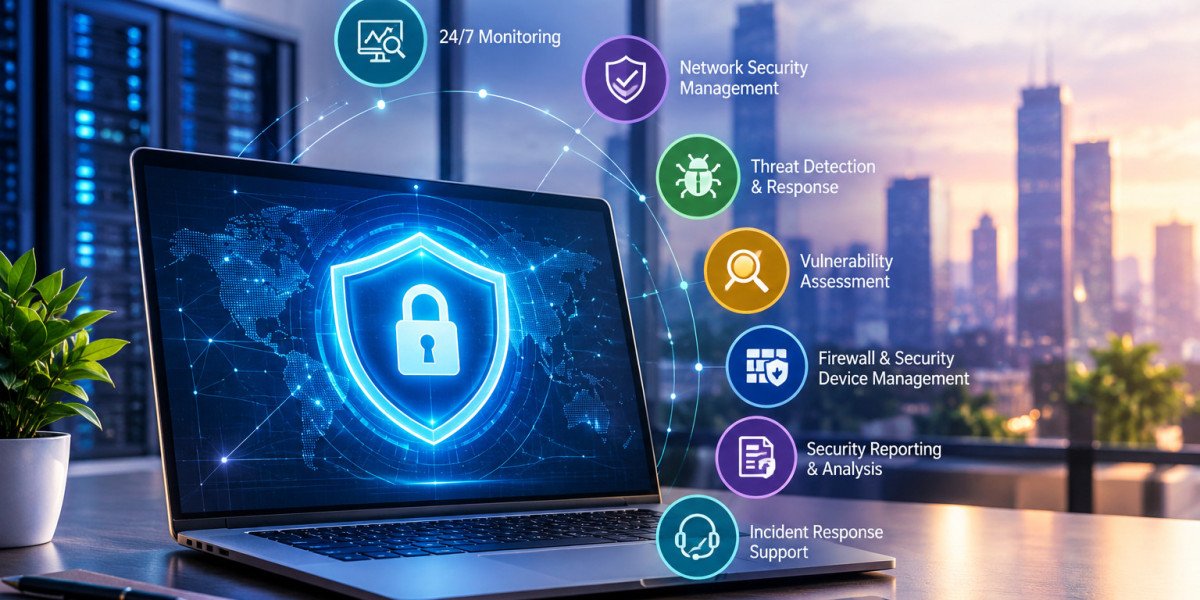
A comprehensive managed security solution may include:
- 24/7 security monitoring to identify suspicious activity
- Network security management to strengthen infrastructure protection
- Threat detection and response for potential security incidents
- Vulnerability assessment to identify weaknesses in IT environments
- Firewall and security device management
- Security reporting and analysis to provide greater visibility
- Incident response support when security events occur
The exact services can vary depending on the provider and the organization's infrastructure, industry, and security requirements.



 See What Fireplace Deals Tricks The Celebs Are Making Use Of
 القوة الخفية للمكونات الطبيعية في العناية بالبشرة: دراسة علمية لأهم المستخلصات الطبيعية
 Anavar Results After 2 Weeks: What You Want To Anticipate
 Transforming Businesses Through Award-Winning Business and Technology Consulting


